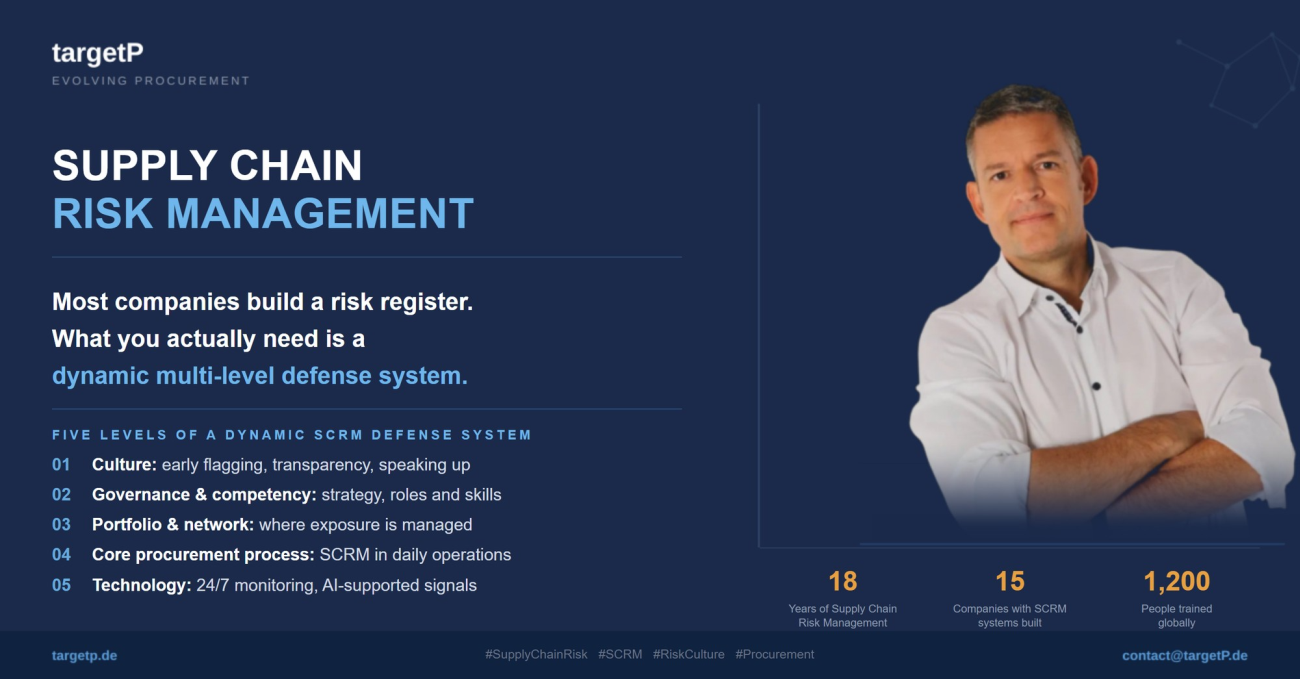
🛡️ Most Companies Build a Risk Register. What You Actually Need Is a DYNAMIC Multi-Layer-Defense Risk Management. The well-known and widely used 3 Lines of Defense model was developed for institutional risk management in finance. Despite years of criticism, too many risk professionals still treat it as the holy grail and believe they can use it across organizations for all kinds of risk management activities. My experience: For SCRM, the model is not usable at all. However, even the big four consulting firms still bother their clients with this ineffective approach. Experienced supply chain (risk) experts never work with it. So do I, and based on 18 years of building SCRM systems across 15 companies, I developed and use a dynamic five-level risk model that translates the lines-of-defense principle into something that actually works in practice: Level 1: SCRM Culture Framework: The foundation everything else rests on. If the culture doesn’t support early flagging, transparency, speaking up, and cross-functional accountability, no process or system will compensate. Culture is not soft. It is the prerequisite. Level 2: Governance & Competency Framework: Strategy, roles, responsibilities, and the skills to execute them. Here, the CPO and procurement leadership define what SCRM means for the organization and how they operationalize it. And this is where the organization becomes agile and responsive. Level 3: Category & Supplier Portfolio/Network Management: The analytical core: category and market analysis, supplier portfolio assessment, and a risk-centered sourcing strategy. This is where procurement teams actively manage exposure. Level 4: Core Process Framework: SCRM embedded into daily procurement operations: supplier qualification and onboarding, sourcing and re-sourcing decisions, and ongoing supplier network management Level 5: Technology Framework: Digital supply chain monitoring running 24 hours a day, 365 days a year. AI-supported signal detection, automated alerts, pattern recognition, scenario modeling, impact analytics. Technology does not replace human judgment. The critical principle behind this model: These five levels are not silos. Insights from the process level feed back into portfolio strategy. The technology layer supports all operational levels simultaneously. The culture layer at the top is why it all works under pressure. SCRM is never static. The moment you treat SCRM as a project, you have already fallen behind. Forever! Now, let’s turn those lessons into capability. Build people and organizations who are ready to act. My training/workshop will perfectly prepare you for it. Hi. I am Jan, your SCRM Builder. Not a consultant who theorizes about risk. A procurement leader and risk practitioner who has built 15 SCRM programs globally, trained 1,200 people, and led procurement and risk organizations through crisis. I share what works and help you build an effective SCRM. I work globally.

 Deutsch
 English